
CREST CERTIFIED API TESTERS
API Penetration Testing Services in Australia
Penva Security delivers CREST-certified, manual API penetration testing for Australian businesses — testing REST, GraphQL, SOAP and mobile/backend APIs for broken authorisation, authentication weaknesses, exposed data, rate-limiting gaps and business logic flaws that automated scanners and AI-only tools often miss.
Every API security test is performed by a human OSCP- and CREST-qualified offensive security expert, delivered with an audit-ready report for ISO 27001, SOC 2, PCI DSS, HIPAA and APRA CPS 234 — and includes a free remediation retest within 60 days.
Certified API Testers
Audit-Ready API Reports
Manual API Testing
What Is API Penetration Testing?
API penetration testing is a controlled, manual security assessment where CREST-certified ethical hackers simulate real-world attacks against your REST, GraphQL, SOAP, mobile and backend APIs. The goal is to identify exploitable API vulnerabilities such as broken object level authorisation, broken authentication, excessive data exposure, mass assignment, rate-limiting weaknesses, insecure CORS and business logic abuse before attackers find them.
Unlike automated API scanning, a true API penetration test validates how endpoints behave across users, roles, tenants, tokens and workflows. A skilled tester chains low-severity API issues into high-impact attack paths and produces a short, prioritised list of confirmed, exploitable findings with proof-of-concept evidence, business impact and developer-ready remediation guidance.
For Australian businesses, API penetration testing is strong evidence for ISO/IEC 27001:2022 controls A.8.8 and A.8.29, SOC 2 Trust Services Criterion CC7.1, PCI DSS Requirement 11.4, APRA CPS 234, and customer security reviews.
To understand our wider security service, visit our penetration testing services at Penva Security.
When You Need an API Pentest
Most Australian businesses engage Penva Security for one of six clear API risk triggers – each maps to a compliance requirement, customer assurance request, or high-impact security event.
Pre-Launch Assurance
Annual Compliance
After Major Changes
Vendor Security Questionnaires
APRA CPS 234
Post-Incident Review
API Penetration Testing Approach
Every Penva Security API engagement follows the OWASP API Security Top 10, OWASP Web Security Testing Guide, NIST SP 800-115, and PTES. We test REST, GraphQL, SOAP and backend APIs the way attackers do: by chaining authorisation, token, object, workflow and data exposure issues to demonstrate real business impact.
-
OWASP API Security Top 10 Testing
Coverage of the OWASP API Security Top 10, including BOLA, broken authentication, object property authorisation, unrestricted resource consumption and broken function-level authorisation.
-
BOLA, IDOR & Access Control
Testing whether users can access, modify or delete API objects, records or tenant data they should not control.
-
JWT, OAuth & Session Weaknesses
Checking token handling, JWT validation, OAuth flows, refresh tokens, expiry, replay risks and account takeover paths.
-
Authentication & Rate-Limiting Flaws
Testing login flows, MFA-dependent API calls, brute-force protection, OTP handling and unrestricted resource consumption.
-
Broken Function-Level Authorisation
Identifying privilege escalation paths where lower-privileged users can call admin, internal or hidden API functions.
-
REST, GraphQL & SOAP API Testing
Security testing for REST, GraphQL, SOAP, mobile backend and internal/external API endpoints.
-
Business Logic & Workflow Abuse
Manual testing for payment, booking, onboarding, approval, invite, subscription and role-change workflows that scanners cannot understand.
-
SSRF & Internal Exposure
Testing API parameters, webhooks, file parsers and integrations for SSRF paths that may expose internal services.
-
CORS, Headers & Misconfigurations
Verifying CORS, TLS/SSL, security headers, debug endpoints, verbose errors and insecure API gateway configurations.
-
Injection, Mass Assignment & RCE
Testing SQL/NoSQL injection, command injection, insecure deserialisation, mass assignment and remote code execution paths.
Our Four-Phase API Pentest Process
Aligned to the OWASP API Security Top 10 2023, OWASP WSTG v4.2, NIST SP 800-115, and the Penetration Testing Execution Standard (PTES).
Work closely with your team to identify exactly what needs to be tested, e.g. a website, mobile app, or internal system, and establish clear boundaries before testing begins. This phase ensures all stakeholders are aligned on what's in scope, reducing miscommunication and delays.
A penetration test execution phase validates real-world risk by actively finding, exploiting, and confirming vulnerabilities, then demonstrating impact with controlled proofs-of-concept. Results are cleaned up, evidence collected, and delivered as a prioritized report with remediation guidance.
Our pentest reports are designed to help you pass audits, with a clear executive summary, CVSS 3.1 severity ratings, and formal attestation to meet SOC2, ISO 27001, PCI DSS, and HIPAA compliance requirements.
Once the team resolves the identified vulnerabilities, a focused retest is performed to verify the fixes and deliver an updated report reflecting the remediation status.
Benefits of API Penetration Testing Service
With Penva’s human-led, AI-assisted API penetration testing services, you can find exploitable API vulnerabilities before attackers do, protect customer data, strengthen client and stakeholder confidence, and prove your API security posture with a clear, audit-ready report.
Find Hidden Weaknesses Before Hackers Do
Penetration testing uncovers hidden weaknesses in your system before real attackers can exploit them, allowing you to address issues promptly.
Avoid Costly Data Breaches
A single cyberattack can lead to stolen customer info, lawsuits, or fines. Penetration testing helps prevent this.
Meet Legal Requirements & Compliance in Australia
Industry standards (such as ISO 27001) and Australian regulations, including the ACSC Essential Eight and the Privacy Act 1988, mandate regular security checks. Penetration testing ensures compliance and helps avoid fines and data breaches.
Build Customer Trust
Customers feel safer knowing you care about their data, and It boosts your reputation as a secure and reliable business.
Penva vs AI-Only and Generic Pentest Firms
Fully AI-driven scanners and autonomous pentesting platforms find known patterns at machine speed – but they consistently miss the vulnerabilities that cause real breaches. Here’s how Penva Security compares.
What You Receive After an API Penetration Test
You receive an audit-ready API penetration testing report with confirmed vulnerabilities, proof-of-concept evidence, affected endpoints, CVSS risk ratings, business impact and developer-ready remediation guidance, giving your team and stakeholders clear evidence of your API security posture.

Penetration Test Report
A comprehensive document detailing identified vulnerabilities, potential risks, and prioritized recommendations.
Includes Executive summary alongside technical evidence like attack paths and severity scores (CVSS) for your IT team.

Remediation Plan and Support
Provides step-by-step instructions and direct collaboration with the dev team to implement fixes, ensuring risks are eliminated.
If required, receive a follow-up report confirming all issues are resolved for accountability and compliance.

Certification of Testing
Official validation that your systems were rigorously tested and meet industry security standards.
Offers formal documentation (e.g., compliance with GDPR, PCI DSS) to demonstrate due diligence to clients, auditors, or regulators.
Audit-Ready for Every Major Framework
Every Penva Security report is purpose-built to satisfy auditors, with the executive summary, CVSS 3.1 scoring, evidence appendix, and formal letter of attestation that compliance assessors require.
ISO/IEC 27001
SOC 2 Type II
PCI DSS v4.0
APRA CPS 234
Essential Eight
HIPAA
GDPR & Privacy Act
ST4S
Pentest Results that Pass Audits
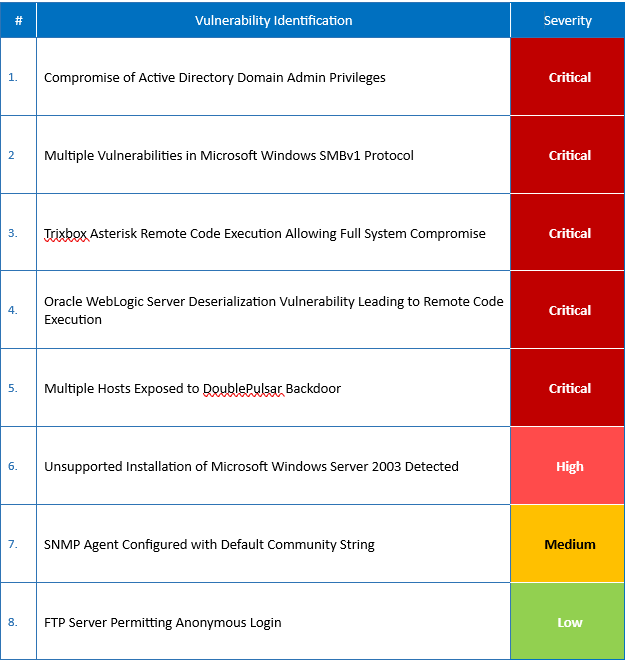
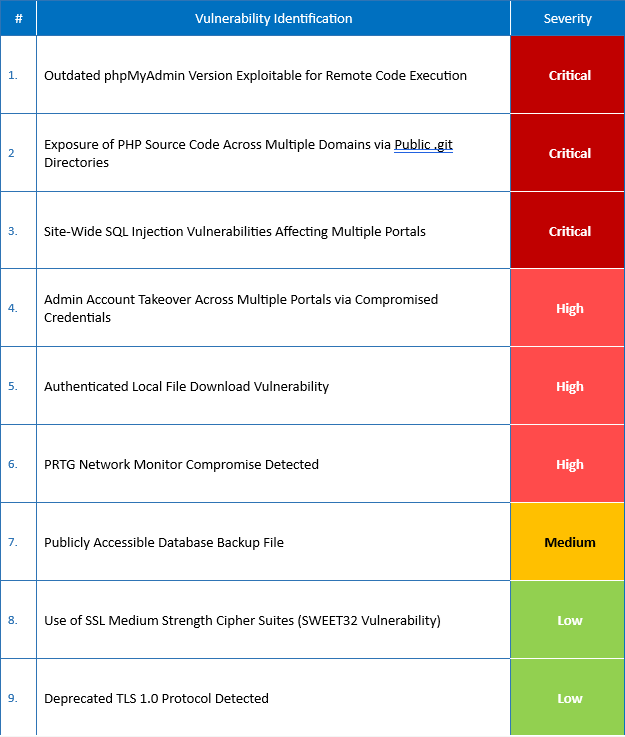
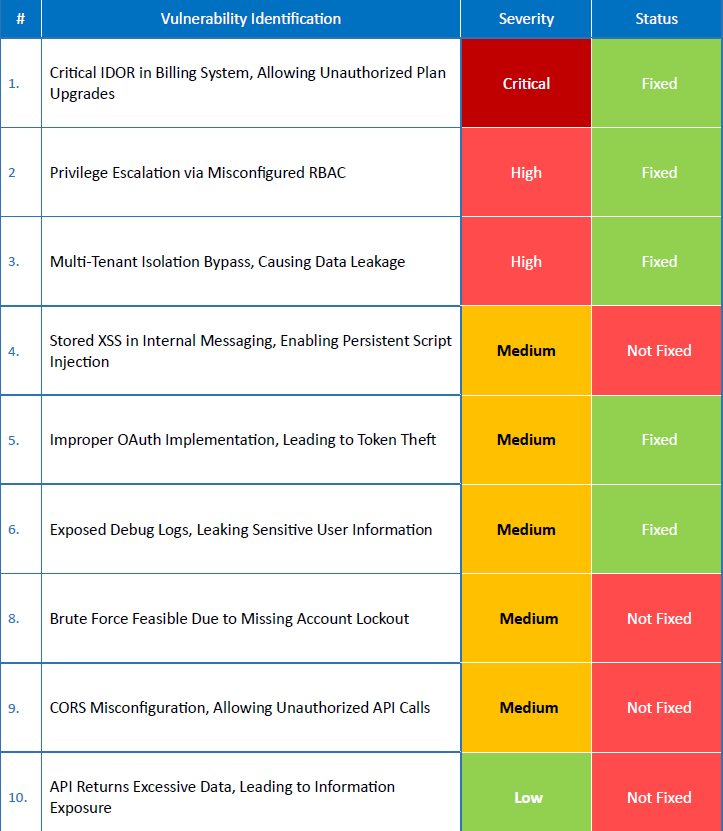
How Penva Security helped businesses pass ISO 27001 and SOC 2 audits with penetration testing reports that satisfied assessors, closed critical gaps, and gave clients the confidence to scale securely.
Although the client approached us only for compliance, we identified serious security gaps and helped secure their application. This proactive assessment demonstrates a strong commitment to data protection, risk mitigation, and adherence to internationally recognized security standards.
The findings provide clear, actionable insights to strengthen the application’s security posture, ensuring it meets SOC 2 trust principles, especially around data confidentiality, availability, and integrity.
Our findings enabled the client to prioritize remediation, strengthen their internal security posture, and prevent potential exploitation that could have severely impacted operations and data integrity.
Why Choose Us
We have partnered with organizations across critical sectors, including finance, education, e-commerce, and healthcare, to enhance their security posture, meet compliance requirements, and confidently pass audits.
We’ve identified critical vulnerabilities in 70% of tested applications, including server compromises and leaked credentials, and helped secure their applications and infrastructure.
Accreditations & Certifications


Brand Name
Certification
Certification Worth
OSCP by Offensive Security
OSCP+ by Offensive Security
The OSCP (Offensive Security Certified Professional) is a highly regarded certification that validates practical penetration testing skills and is globally recognized by employers and regulators.
CREST Practitioner Security Analyst (CPSA)
CREST Registered Penetration Tester (CRT)
CREST partners with national bodies in the UK, US, Australia, and Singapore, ensuring global recognition and compliance with the highest cybersecurity standards.
CRTO by Zero-Point Security
This certification demonstrates the ability to think and act like a real attacker, simulating advanced cyberattacks to help organizations identify and remediate hidden weaknesses before they can be exploited.
Penva Security holds globally recognised, specialized penetration testing certifications that take years to earn.
Reviews and Clients
Michael Wendland
Partner at Bonsai
Reliable and professional penetration testing partner
Penva Security provided a quick and efferent pentest report that satisfied our needs and certification criteria. I would highly recommend them for penetration testing, and will be using his services again in the future.

Stuart Cox
Creative Director at NorthBase
Professional, communicative, and highly reliable testers
Penva Security conducted a penetration test of our webapp and produced a report of security issues. The team was professional and communicated well throughout, including giving us the expected timeline for the work and keeping us up-to-date as we progressed. The report was well written and I can recommend them to anyone looking for penetration testing.
Daniel Scocco
Founder at InstaDelivery
Working with third or forth time with Penva Security
This is the third or fourth time we work with Penva Security. They always delivers timely and great work. One of the best security experts I know.
Our Team's Certification
Our team holds industry-recognized pentest certifications that take years to achieve.


API Penetration Testing - Common Questions
Direct answers to the API security testing questions Australian businesses ask most often.